ISO 27001 · Fast Track · Certification
The fastest way to get ISO 27001 certified
Keep the scope tight, generate your documentation from how you already work, and book the auditor on day one. Here's the fastest realistic route to ISO 27001, and how the Genroks Fast Track gets companies certified in about 10 days.
Genroks Team · 20 October 2026
The short answer
The fastest way to get ISO 27001 certified is to:
- Keep the scope tight. Certify the products, teams and systems your clients actually ask about, not the whole group.
- Generate your documentation from how you already work. Don't write the management system from blank templates.
- Book an accredited certification body on day one. Auditors plan their calendars weeks ahead. Don't wait until you feel ready.
- Run the risk assessment, internal audit and management review early. The auditor needs to see a management system that works, not just documents.
- Let people who have done it many times do the work, and have them with you at the audit.
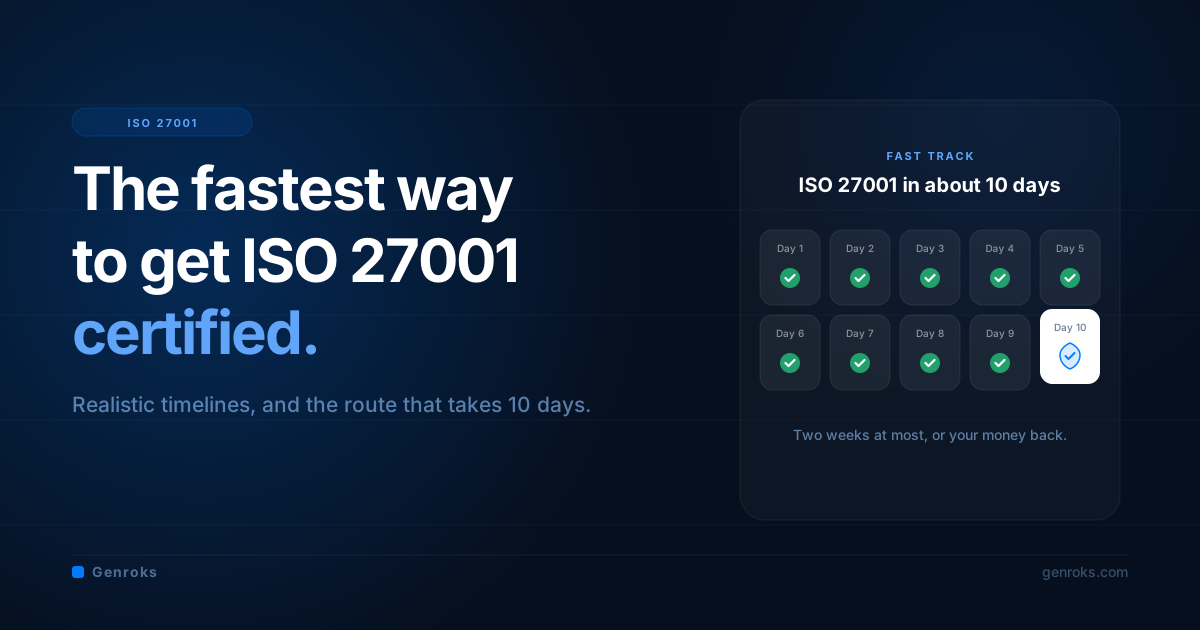
That's what the Genroks Fast Track does. Our experts do the work on your Genroks platform, coordinate an accredited certification body and attend the audit with you. You're certified in about 10 days, two weeks at most, or you get your money back.
How long does ISO 27001 usually take?
It depends far more on how you do it than on the size of your company.
| Route | Typical timeline | Your team's time |
|---|---|---|
| Traditional consultant | Around 6 months, often longer | Weeks of workshops and document reviews |
| Templates, done yourself | 6 to 12 months | Months of writing documents |
| Genroks platform | Audit-ready in a few weeks to a few months | A few hours a week |
| Genroks Fast Track | Certified in about 10 days, two weeks at most | Our experts do the work. You answer questions and approve. |
Where the time actually goes
ISO 27001 isn't slow because the standard is long. It's slow because of how most companies approach it.
- Writing documents from scratch. ISO 27001 requires documented information such as the scope of your management system, an information security policy, a risk assessment and risk treatment plan, a Statement of Applicability, and the policies behind the Annex A controls you apply. Written by hand, that takes months. On Genroks, your policies are ready when onboarding is done, built on your real processes, systems and tools.
- Collecting evidence by hand. Screenshots chased over email. Connect your tools, and Genroks collects most evidence automatically and asks the right person for the rest.
- Waiting for an auditor. Certification bodies plan weeks ahead. Booking only once you're ready adds weeks you didn't need to lose.
- Gaps nobody owns. A spreadsheet of gaps doesn't close itself. Every gap needs an owner and a deadline.
- A scope that's too big. Every extra location, team or product adds controls to implement and time to the audit.
The fastest route, step by step
1. Define the scope
Decide which products, teams, locations and systems are in. A tight scope is faster to implement and to audit, but it has to cover what your clients care about. If a client is asking about your software product, the scope should cover the product, the team that builds and runs it, and the systems it runs on.
2. Find your gaps
Answer plain-language questions about how you work. Genroks maps your answers against every clause of ISO/IEC 27001:2022 and all 93 Annex A controls, and shows exactly what's missing.
3. Approve your policies and Statement of Applicability
Your policies, risk register and Statement of Applicability build themselves from your answers. You review and approve them. Nothing is approved without you.
4. Close the gaps that matter
Typical quick wins: multi-factor authentication everywhere, a process for people joining and leaving, tested backups, access reviews, security awareness training and a list of your suppliers. Every remaining gap becomes a task with an owner.
5. Show the system working
Before the certification audit, the auditor expects to see your management system in operation: a completed risk assessment, an internal audit, a management review and records of the controls you run. Planned from day one, these take days, not months.
6. Pass the Stage 1 and Stage 2 audits
Stage 1 reviews your documentation and readiness. Stage 2 checks that your controls work in practice. With Fast Track, Genroks coordinates the certification body so both stages happen close together, and our experts attend the audit to answer the hard questions.
7. Stay certified
An ISO 27001 certificate is valid for three years, with a surveillance audit every year. Genroks keeps the evidence, reviews and reminders running, so the next audit isn't another scramble.
Is a fast ISO 27001 certificate a real certificate?
Yes. The speed comes from the preparation, not from skipping steps in the audit. Your certificate is issued by an independent, accredited certification body after the same Stage 1 and Stage 2 audits every company goes through.
Genroks is not a certification body. We prepare you, coordinate the audit and keep you compliant afterwards. Whoever you work with, check that your certificate will be accredited: issued by a certification body that is accredited by a national accreditation body that signed the IAF Multilateral Recognition Arrangement. Enterprise clients and public tenders check this.
Which company can get you ISO 27001 certified fastest?
Look for three things:
- Someone does the work for you. A template library or a checklist still leaves the writing to you.
- The certification body is part of the plan. Waiting for an audit slot is where many fast projects stall.
- A guarantee on the timeline. If a provider is confident in its speed, it should put money behind it.
The Genroks Fast Track does all three. Our experts do the work on your Genroks platform, coordinate an accredited certification body and attend the audit, and you're certified within two weeks or you get your money back. Fast Track is a fixed quote per company, with no hourly billing. The certification body's fee is paid directly to the certification body.
If there's no deadline, the Genroks platform on its own (€299 a month for ISO 27001) gets most teams audit-ready in a few weeks to a few months, at a few hours a week.
Real timelines from Genroks customers
- Topoms: ISO 27001 in two weeks, to unlock enterprise deals.
- Techtonnik: certified in 16 days, with almost none of their internal time.
- COMIT: the complete documentation package in 18 days, to close a $100k+ US enterprise deal.
- Govin: ISO 27001 in three weeks, to meet a client deadline.
Frequently asked questions
How long does ISO 27001 certification take?
With a traditional consultant, around six months or more. On the Genroks platform, most teams are audit-ready in a few weeks to a few months. With the Genroks Fast Track, companies are certified in about 10 days, two weeks at most.
Can you get ISO 27001 certified in two weeks?
Yes, if the work is done for you and the certification body is lined up from the start. That's how the Genroks Fast Track works, and it comes with a money-back guarantee.
How much does ISO 27001 cost?
On Genroks, the platform is €299 a month for ISO 27001, and Fast Track is a fixed quote based on your company's size and scope. The certification body's audit fee is separate and varies by country and scope.
Is ISO 27001 mandatory?
Not by law. In practice, many enterprise clients, public tenders and partners make it a condition of doing business.
Should we get ISO 27001 or SOC 2?
ISO 27001 is the international certification most European clients and tenders ask for. SOC 2 is the report US customers expect. Most controls overlap, so on Genroks one piece of work counts toward both. See the fastest way to get SOC 2 compliant.
Next step
Book a demo and we'll show you where you stand on ISO 27001 today, and the fastest route from there.