SOC 2 · Audit Prep · Compliance
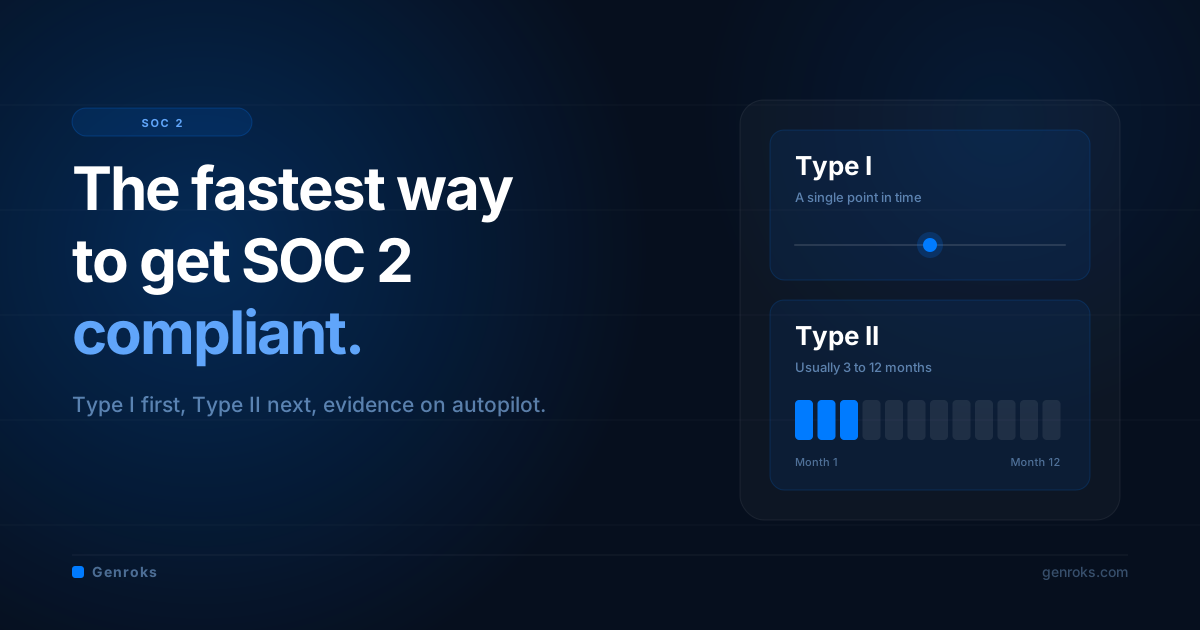
The fastest way to get SOC 2 compliant
Start with a Type I report, scope to the criteria your customers need, and let your tools supply the evidence. Here's the fastest realistic route to a SOC 2 report, and where Type II fits.
Genroks Team · 20 October 2026
The short answer
The fastest way to get SOC 2 compliant is to:
- Start with a Type I report. It checks that your controls are designed properly at a single point in time, so there's no observation period to wait for.
- Scope to what your customers need. Security is always required. Add Availability, Confidentiality, Processing Integrity or Privacy only when you promise them to customers.
- Build policies and controls from how you already work, not from blank templates.
- Connect your tools, so evidence is collected automatically instead of by screenshot.
- Engage a licensed CPA firm early, so your audit is scheduled while you prepare.
- Start the Type II observation period as soon as your controls are running. Many companies choose a 3-month period for their first Type II report.
With Genroks, most teams are audit-ready in weeks: your policies are ready after onboarding, evidence is collected from your connected tools, and we coordinate a licensed CPA firm for you.
Type I or Type II: which is faster?
| SOC 2 Type I | SOC 2 Type II | |
|---|---|---|
| What it checks | Your controls are designed properly | Your controls worked over a period |
| Observation period | None, a single point in time | Usually 3 to 12 months |
| Time to a report | Preparation, then the audit | Preparation, the observation period, then the audit |
| Who asks for it | Customers who need a report soon | Most enterprise customers |
Type I is the fastest way to have a SOC 2 report in hand. Most enterprise customers ultimately want Type II, so the fastest overall route is usually Type I now, to unblock deals, and Type II next. If your customers will accept nothing but Type II, skip Type I and start your observation period as soon as your controls are in place.
Where SOC 2 time goes
- Deciding what's in scope. Which systems, which criteria. An unclear scope means rework later.
- Writing policies. Information security, access control, change management, incident response, vendor management and more. On Genroks, they're ready after onboarding.
- Evidence across the period. Access reviews, change approvals, onboarding and offboarding records, training completions. Collected by hand, this is where months disappear. Connected tools supply most of it automatically.
- Finding an auditor. Only a licensed CPA firm can issue a SOC 2 report, and good firms book ahead.
- Vendors. SOC 2 expects you to review the vendors that handle your customers' data.
The fastest route, step by step
1. Choose your criteria and scope
Security is required. Add other Trust Services Criteria only when your contracts or customers call for them. Scope the system that serves your customers: the product, the infrastructure it runs on and the people who run it.
2. Assess where you stand
A readiness assessment maps how you work today against the criteria and shows your gaps. On Genroks, that's a guided set of plain-language questions.
3. Put policies and controls in place
Close gaps with guided tasks, each with an owner. Typical work: multi-factor authentication, access reviews, change management, logging and monitoring, incident response, security training and vendor reviews.
4. Connect your tools
Connect Google Workspace, AWS, GitHub and your other tools. Genroks gathers most evidence automatically and asks the right person for the rest.
5. Get your Type I report
The CPA firm checks that your controls are designed properly at a point in time. Genroks organises the evidence and coordinates the audit.
6. Run the observation period and get Type II
Your controls keep running, and Genroks keeps collecting evidence across the whole period. At the end, the CPA firm tests how your controls worked and issues your Type II report.
7. Share it and renew it
Share the report under NDA through your Trust Center, and renew it every year.
Already have ISO 27001? You're most of the way there
ISO 27001 and SOC 2 overlap heavily: risk assessment, access control, change management, incident response and vendor management. Genroks maps what you've already done to the Trust Services Criteria, so you only close the difference.
Who issues a SOC 2 report?
A licensed CPA firm, under AICPA standards. Genroks prepares you, organises the evidence and coordinates the audit, but doesn't issue the report itself.
How Genroks gets you to SOC 2 faster
- Policies ready after onboarding, built on your real processes and systems
- Controls mapped to the Trust Services Criteria, with every gap assigned
- Evidence collected automatically from connected tools, through the whole observation period
- A licensed CPA firm coordinated for you
- A Trust Center to share your report with customers
The platform is €299 a month for SOC 2, or €450 a month for SOC 2 and ISO 27001 together.
Frequently asked questions
How long does SOC 2 take?
With Genroks, most teams are ready for a Type I audit in weeks. Type II adds an observation period of usually 3 to 12 months, and many companies choose 3 months for their first report.
Is SOC 2 mandatory?
No law requires it. In practice, US customers, especially larger ones, ask for a SOC 2 report before they sign.
Which Trust Services Criteria do we need?
Security is required. Availability, confidentiality, processing integrity and privacy are added based on what you promise your customers.
Should we get SOC 2 or ISO 27001?
SOC 2 is the report US customers expect. ISO 27001 is the international certification most European clients and tenders ask for. On Genroks, one piece of work counts toward both. See the fastest way to get ISO 27001 certified.
Next step
Book a demo and see where you stand on SOC 2 today, and what Genroks builds for you from there.